NDA project
[ *** Passport ]
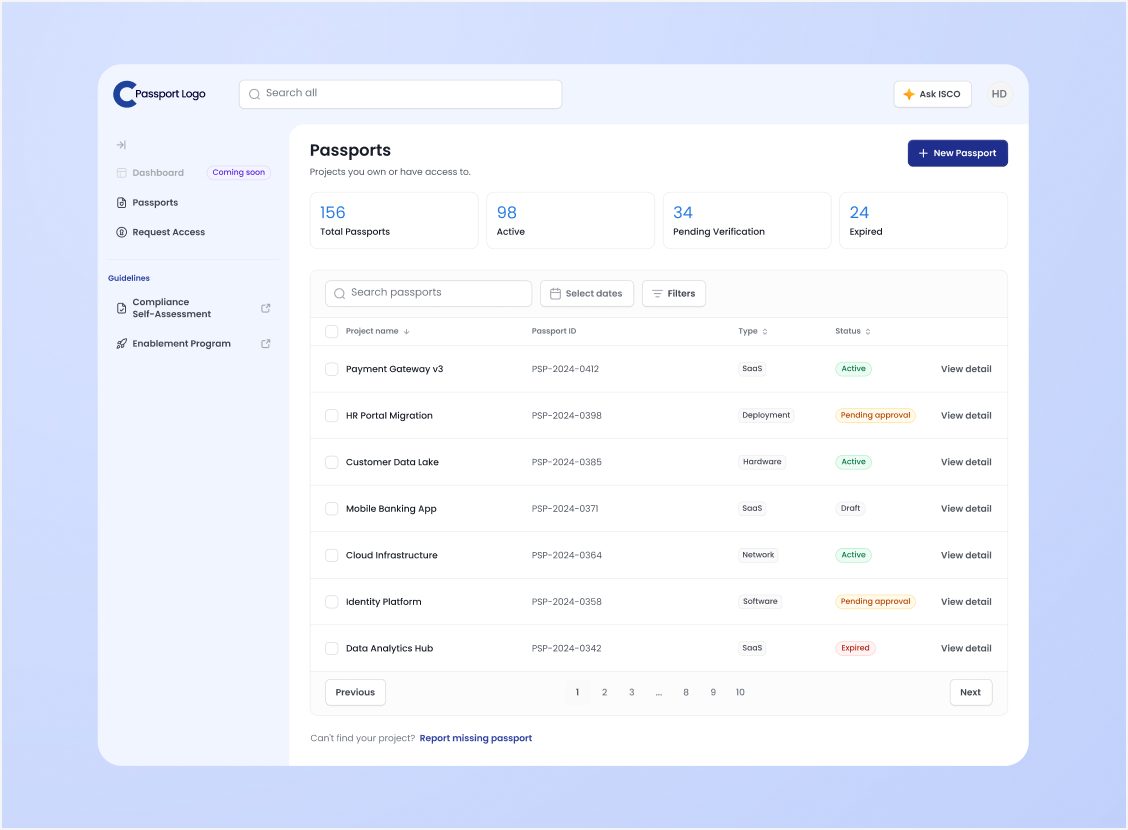
An internal cloud governance dashboard for an NDA enterprise client: app passports, compliance reviews, privacy assessments and access requests in one place.
Case study
Overview
An internal dashboard for a large enterprise, under NDA. It brings cloud governance into one place: application “passports”, security compliance reviews, privacy assessments, access roles and cloud account requests.
The problem
Before this, governance work lived in forms, emails and spreadsheets. Teams didn’t know where their application stood, which section needed them, or who had to approve what. Every request felt like sending a letter and hoping.
The users are engineers and project owners. They are busy, smart and allergic to paperwork.
My role & team
Product designer, working on the platform flows end to end.
Process
- Mapped each workflow as a flow with phases before designing screens
- Built every page on one layout: a header, a banner that explains the page, then the work
- Designed the happy path first, then pending, success and “needs attention” states
Key decisions
Every page answers two questions first
Where does this stand today, and what needs my attention next? The passport profile opens with a line like “3 of 5 sections need attention. Update what you know now and come back when you have the rest.” It takes the pressure off.
Explain roles where you assign them
Owner, manager and viewer each get one plain sentence right next to the choice. Nobody should need a policy document to add a colleague.
Tell people when no human is needed
The Okta integration request shows an automation preview: based on your answers, this can finish without a human in the loop. People love hearing they don’t have to wait for a ticket.
Screen by screen
Passport profile
The home of each application: business criticality, data classification, data residency, deployment details, and who can access the passport.
Security compliance review
A phased flow. Phase 1 reviews what’s not compliant and points out items that can be fixed without an exception. Later phases collect a remediation plan, 3 to 5 milestones, interim risk controls and an owner.
Privacy impact assessment
Landing, create, detail and submitted states, so people always know if their assessment is still a draft or waiting for review.
IAM hub
Manage roles, manage projects, request single sign-on, and create app level or project level roles with settings like “requestable” and “requires owner approval”.
Account vending and project onboarding
Request a new cloud account, set up DNS or ask for firewall rules, then follow the request from submitted to approved.